Recently, I’ve had the extreme pleasure of designing and setting up the challenges for the OSINT category of the Tengucon CTF.
If you want to learn more about Tengucon, you can do so here: https://tengucon.org/
Sadly, I was not in attendance for the event, but I was there in spirit. It was my first time designing and implementing CTF challenges from scratch, so I really hope the players enjoyed it.
Let’s look at the solutions !
1. Operation Monodrome
The challenge starts with this PDF file, which is a mission briefing. In there, we find a list of names, along with an email, or a specific account. For simplicity, we will immediately take a look at the last account of the list, William N., aka “wall0wW1spr”.
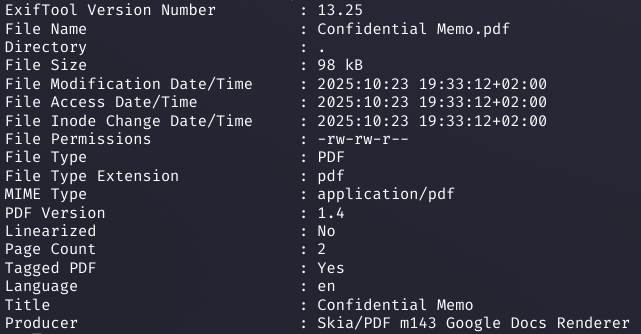
exiftoolfor this PDF doesn’t tell us much
So far, here are our suspects:
- Kamel Ghali:
https://www.sans.org/profiles/kamel-ghali - Mathilde “kallone” R.:
https://github.com/kallone - Tim Krach:
https://www.linkedin.com/in/tim-krach/ - William “wall0wW1spr” N.:
[email protected]
If we look for this username on Github, we quickly find this page. We can confirm it’s the same person, as they use the same email for their commits.
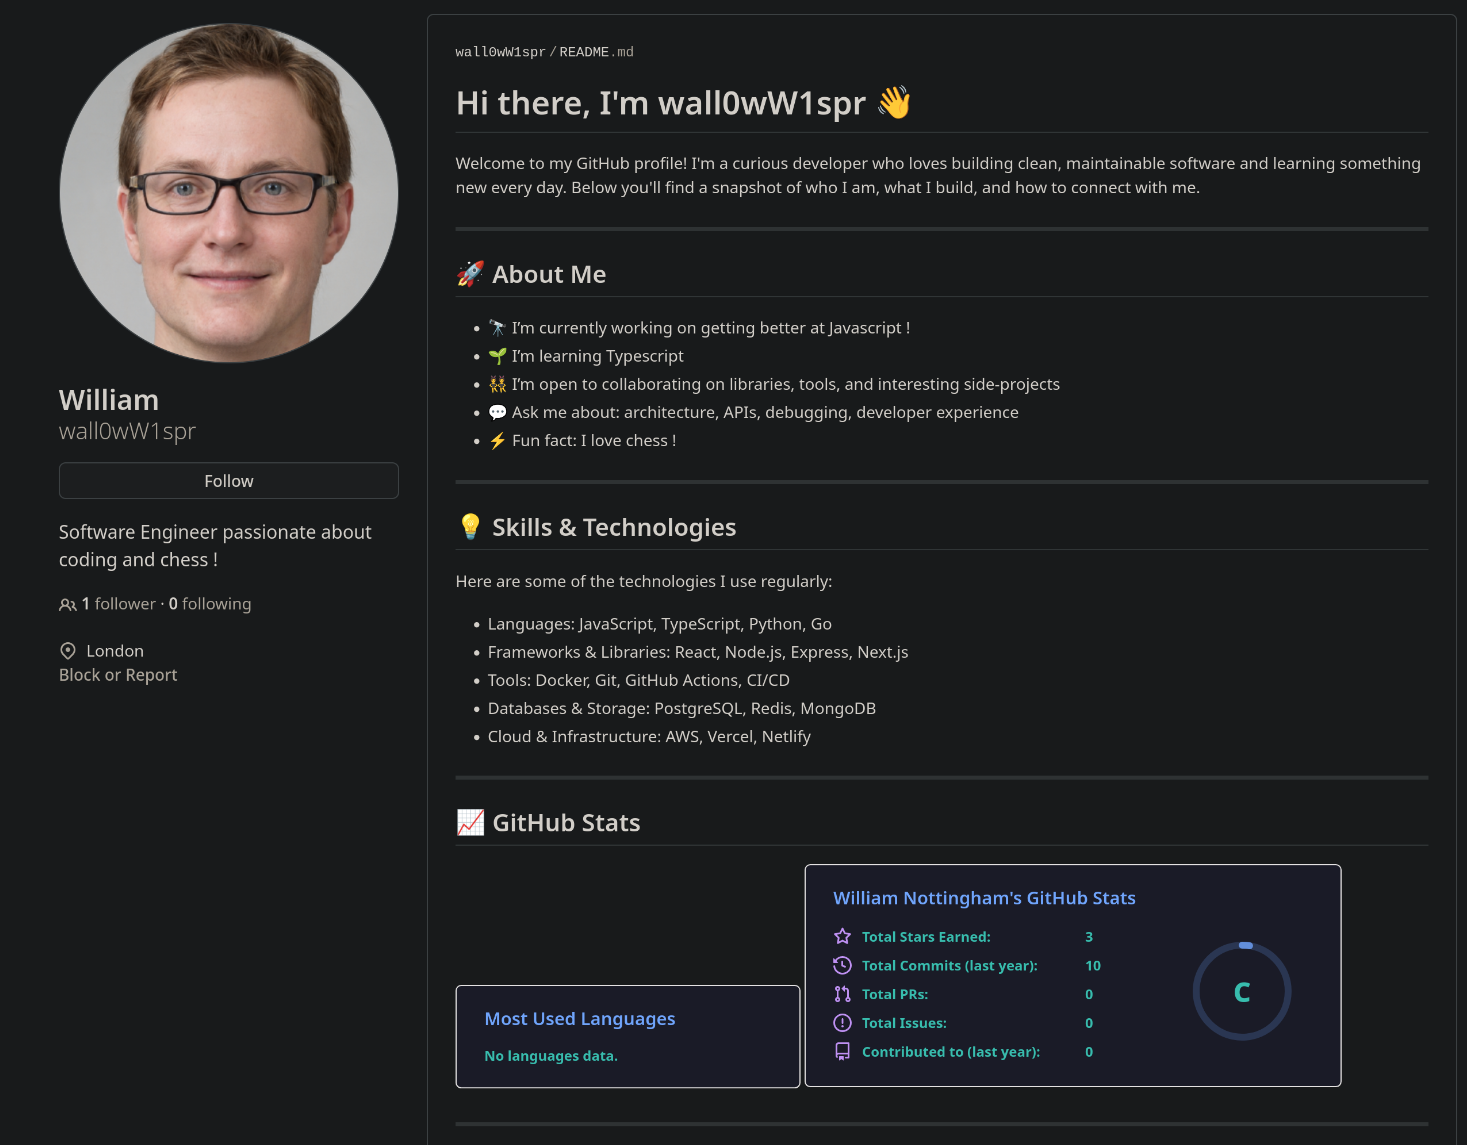
There is a few interesting repos, but we find one in particular that is always interesting. It is the dotfiles repository, containing personal configs and things like that.
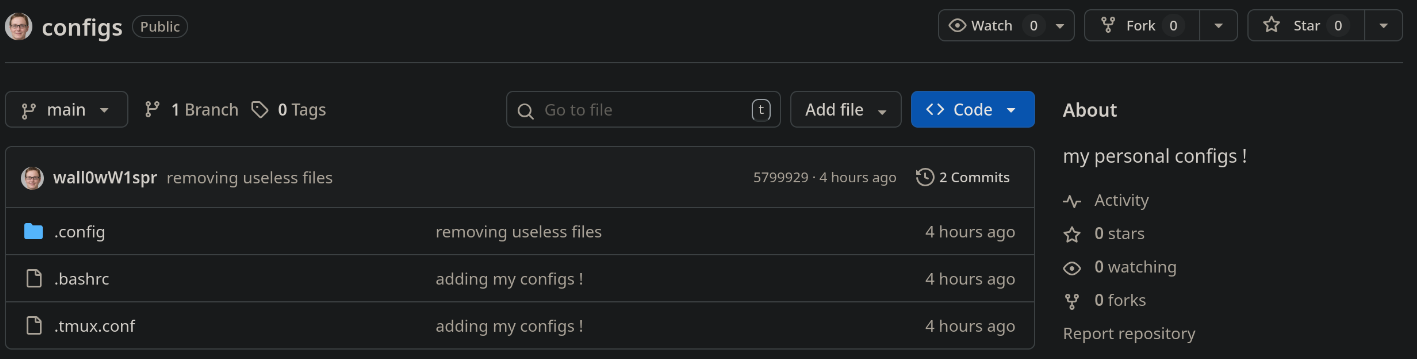
Digging through the logs, we can see there was, at one point, a .ssh/config file:
Host github
    HostName github.com
    User git
    IdentityFile ~/.ssh/id_rsa-ww
    IdentitiesOnly yes

Host gitlab
    HostName gitlab.com
    User git
    IdentityFile ~/.ssh/id_rsa-wn
    IdentitiesOnly yes
This means they also have a gitlab account ! Using the User API, it is then trivial to find the account, since they have the email set as public.
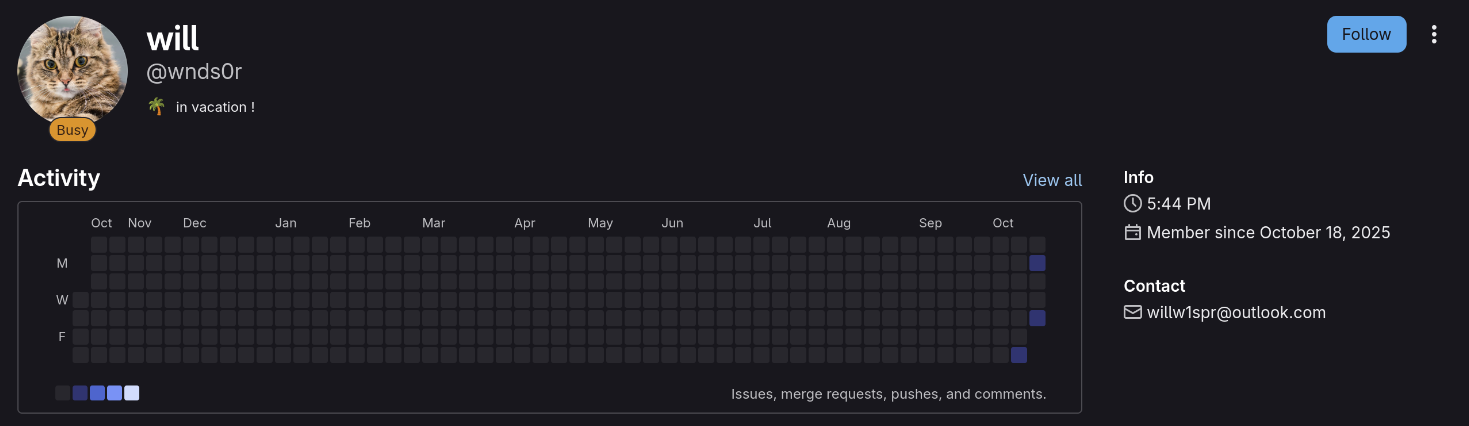
We then finally reach the gitlab page, with the user wnds0r.
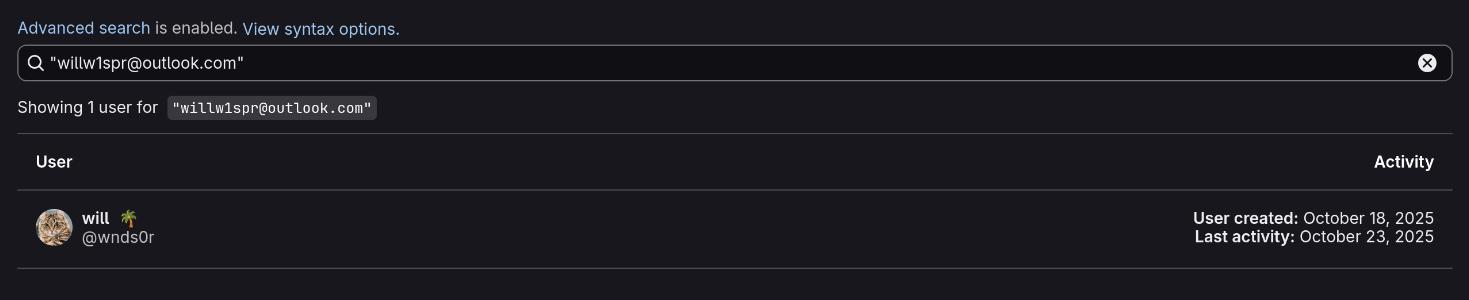
This is our first flag: tenguctf{wnds0r}
2. Digging through files
Thank you for your work ! We will name our target WINDSOR, as it seems fitting. Can you find WINDSOR’s phone number ?
The second challenge prompts us to find our target’s phone number. We keep digging.
Looking at WINDSOR’s repositories, we find one that has many interesting files:
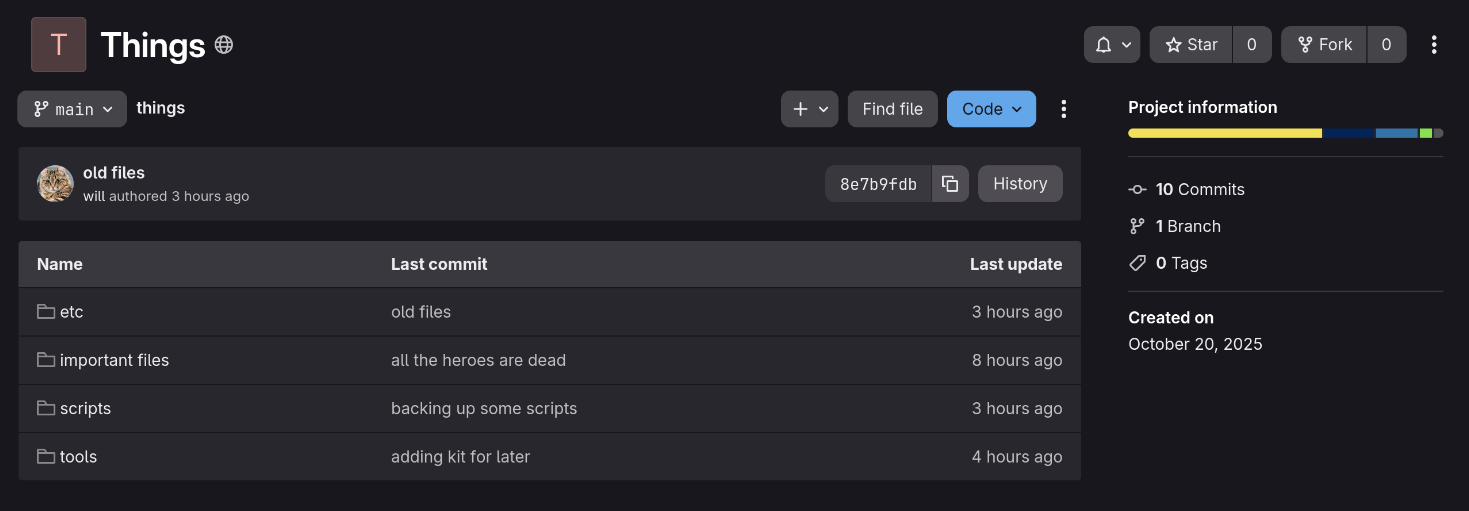
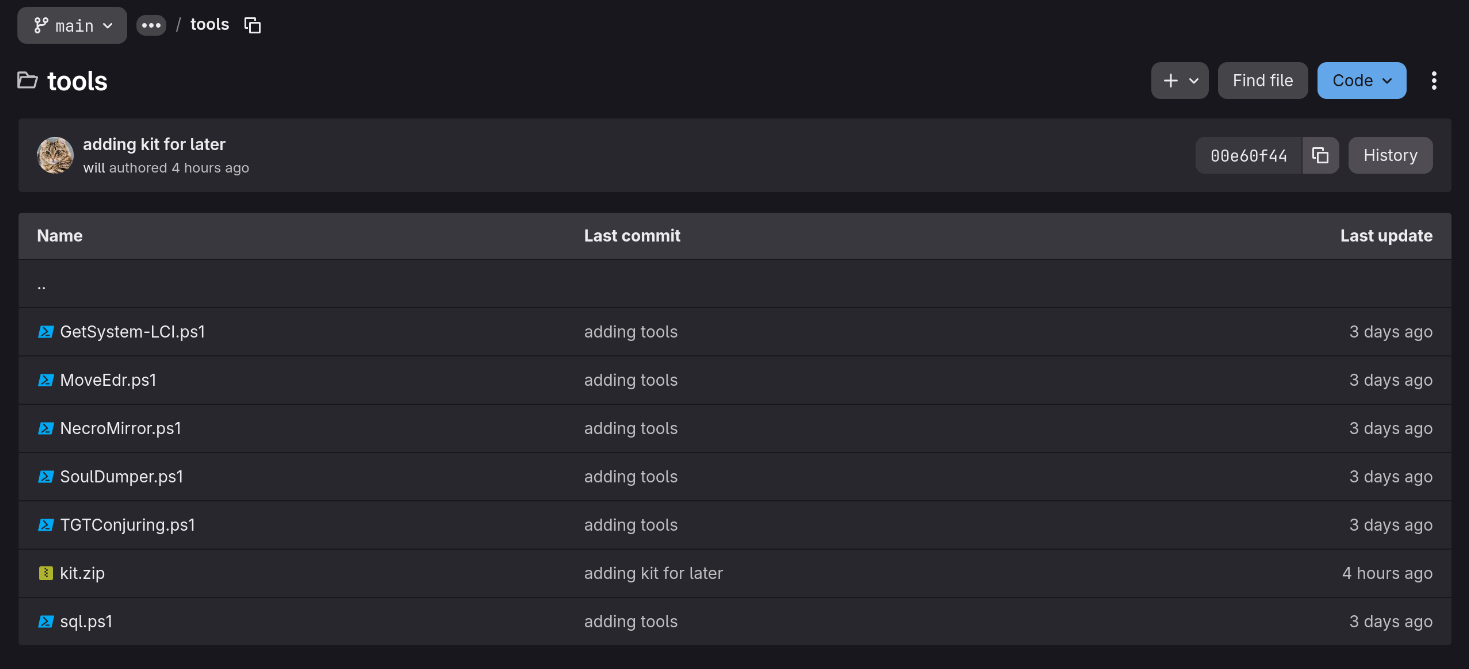
In the tools/ directory, we find a file called kit.zip, among pentesting scripts:
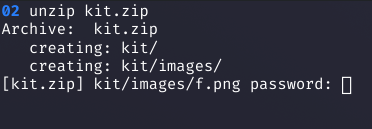
If we download it and try to unzip it, we can see it is password-protected.
We can attempt to brute-force it, like so:
zip2john -s kit.zip

# we recover the following hash:
# kit.zip:$pkzip$5*1*1*0*8*24*7c7d*766435f74e9c312b27fa65c1697ea6fec27c84cb65ba0d6bce020947b1a406d71a64cee4*1*0*8*24*7c7d*d2d0db92d6537f8ad2c78adedf2f4940b96ffcb02b3a749ecf8f9100a0462f2150b651bd*1*0*8*24*7c7d*f352fc24a77bcee4568fd21ba9b2f0f0d7e6f51de48b9c771d0e95c3a0fc937fb90b447b*1*0*0*24*7c7d*95dd5ac34bbd1553b1804ff5d5eef80a2c2ce321e5e6a9c059eabd0e15321fafd3a1f402*2*0*8f*9a*e4d4a018*2fe9*46*8*8f*7ca3*b6f2ef639b52e6ca231322a28daf48e59cdb4af6639b7007b337e836b4e910d5a6944b1f62bcfc6bdbf76d8f063f920641dbd150a2311b1fc4274d494ec587bc425cc99dc51e9d84f2f6506cf7fa95fbd25c6a18e4155545335cfa9dba4839612f81791382a1fe040efcf962faec427b5fbe2462431b4a7c07b7e72f28c511c438b51f8fd925542b959777c262173f*$/pkzip$::kit.zip:kit/TODO.txt, kit/CssSheets/style.css, kit/index.html, kit/images/facebook-logo.png, kit/images/f.png:kit.zip

john --wordlist=/usr/share/wordlists/rockyou.txt hash
We pretty much immediately find that the password is william, after which we can unzip the archive.
Inside, we find a Facebook login page, similar to a phishing kit:
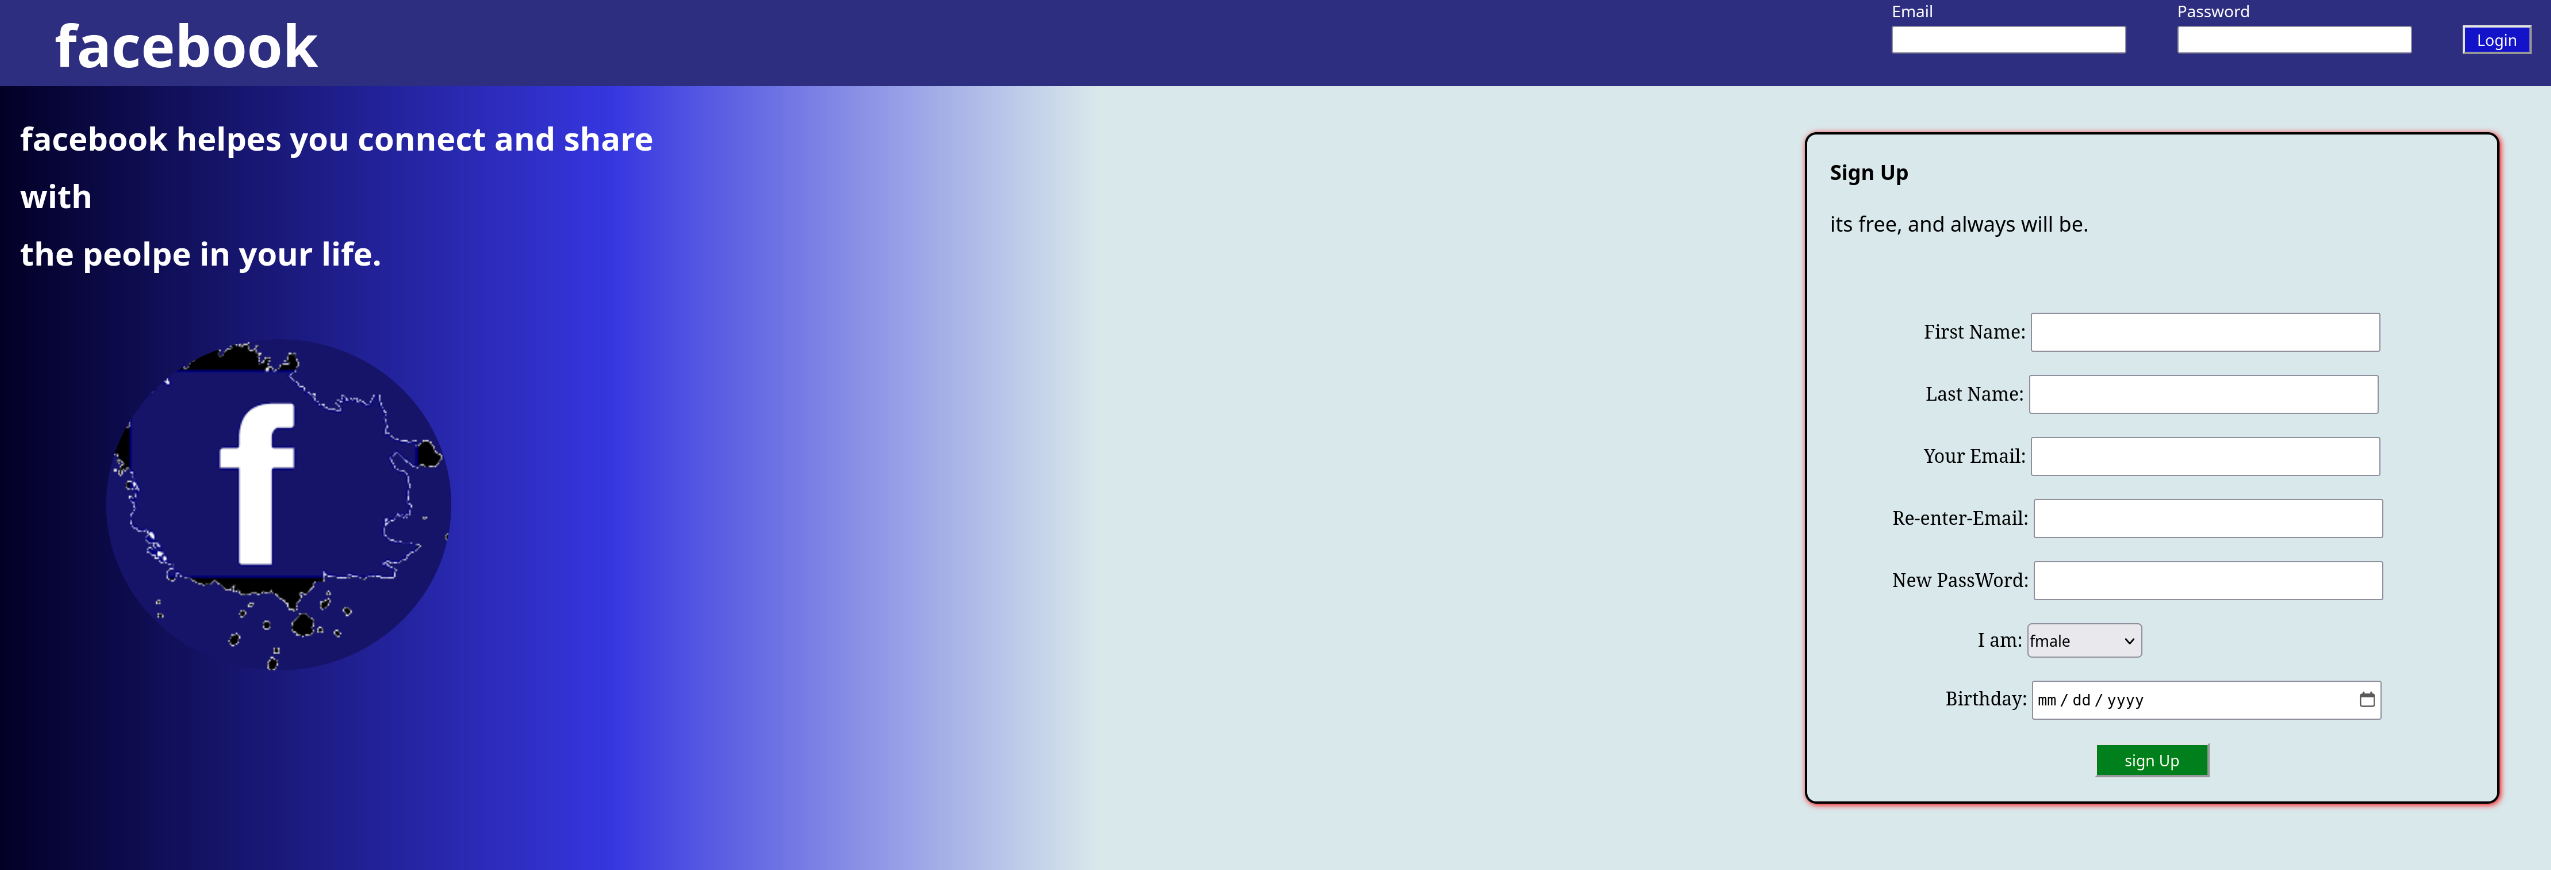
But, more interestingly, we find a TODO.txt file:
Add Telegram bot integration:

1. create account (phone number: 07700900382)
2. add PHP back-end
3. make bot link up with login page
4. start spraying:)
Here, in plaintext, we find our phone number, which is the flag: tenguctf{07700900382}
3. Email intercept
Thank you. This is very valuable intelligence. Using this information, we were able intercept an email, but it is GPG-encrypted. Recover its content, we are looking for a domain, phone number, or another email.
For the third challenge, we’re provided a gpg-encrypted text. Our goal is to recover the contents and find critical intel from it.
Looking again at the repositories we have, we can find that a GPG-private key was mistakenly pushed.
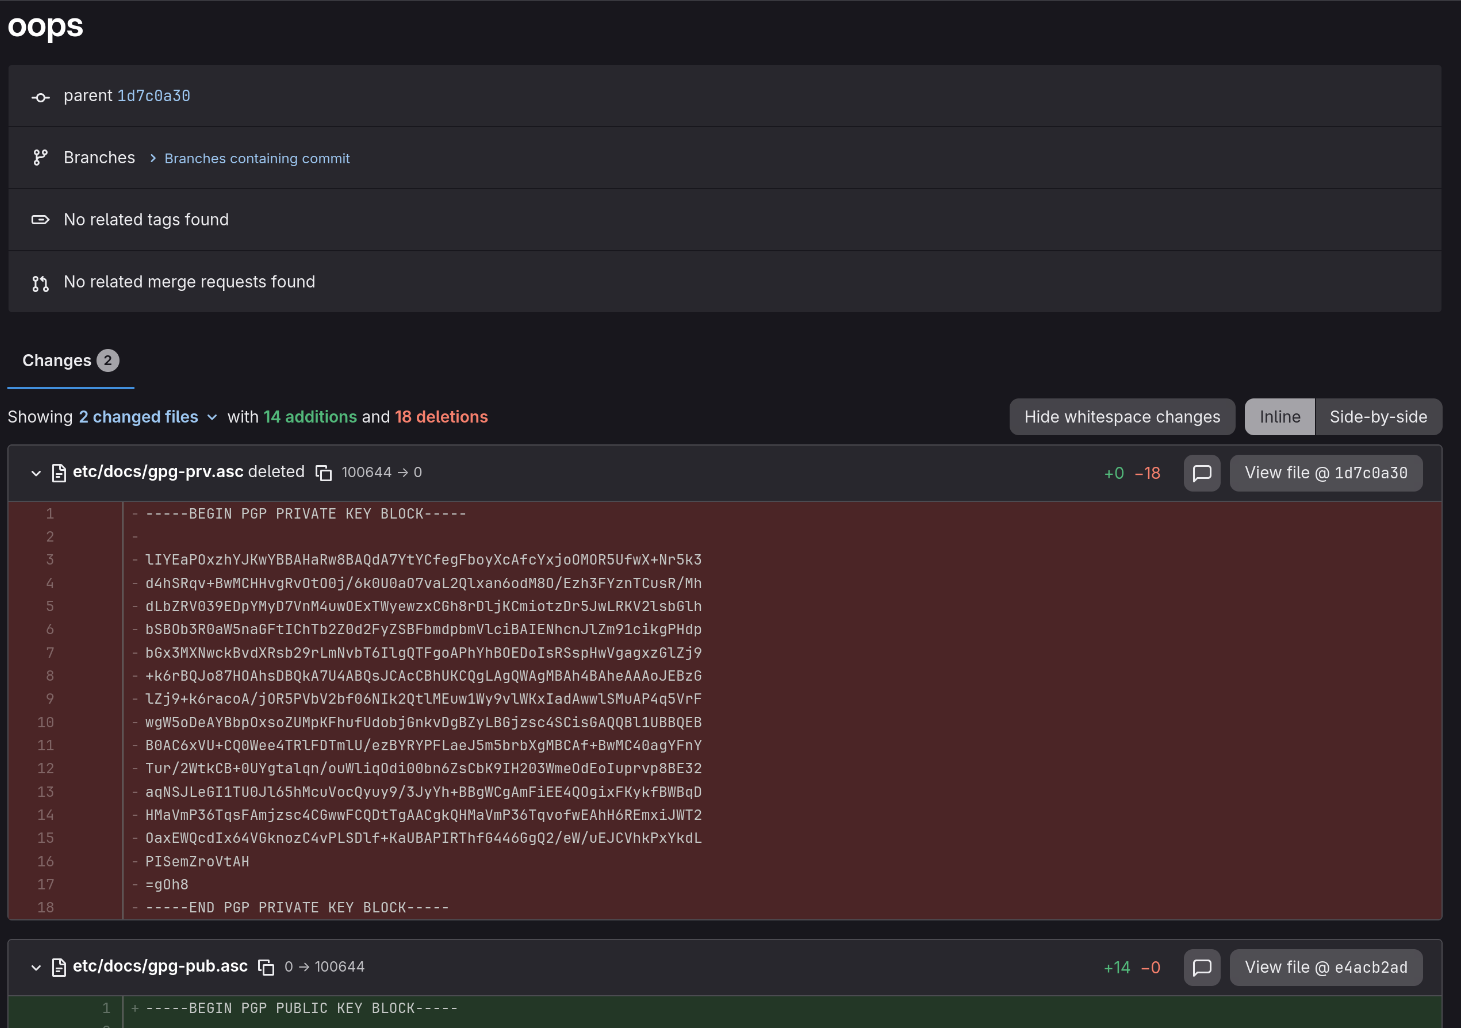
With it, we can try to decrypt the message. However, most GPG (this one too) require a password. To address that, you can simply brute-force with rockyou.txt and you will find the password for the key. Or, you can simply re-use the same password as before, which will work.
This will allow you to see the contents of the message:
From: William Nottingham <[email protected]>
To: djnn <[email protected]>
Subject: Re: working together

Thanks. I'll be in touch after I'm back from vacation.

	From: djnn <[email protected]>
	To: William Nottingham <[email protected]>
	Subject: Re: working together

	It's ready. You can find the address by checking DNS record on MZWGCZYK.tengu.fyi

	Talk to you soon


		From: djnn <[email protected]>
		To: William Nottingham <[email protected]>
		Subject: Re: working together

		Hey,

		I own a couple of domains for throwaway things. I can set it up myself.
		Once it's ready, I'll just send you the logs, or something.

		Just make sure to keep it very low-key.

			From: William Nottingham <[email protected]>
			To: djnn <[email protected]>
			Subject: Re: working together

			What's up ?

			Yeah, that could work. To be honest, I feel like this kind of thing is just easy money.
			We can spray the exploit before it gets patched, and deploy a couple of kits.

			I'll get a leak site going, not sure when yet. We cannot put it on the clear net though, it's too risky.

			Do you have an idea ?
It talks about DNS records. Using the nslookup command, we can check all types of records for this address.
And, if we check TXT records, we find:
$ nslookup -type=TXT MZWGCZYK.tengu.fyi
To make it a bit more obvious, you can also use this CLI tool to make the TXT query
Since it is one of WINDSOR’s projects, it gives a bit of a hint.
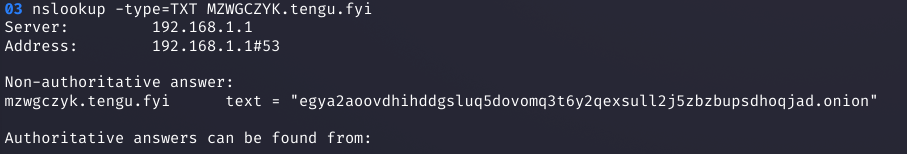
This is our third flag: tengu{egya2aoovdhihddgsluq5dovomq3t6y2qexsull2j5zbzbupsdhoqjad.onion}
4. Peeling the layers…
A
.onionwebsite ! How interesting. Let’s visit it and find out more. What is the hacking group’s name ?
We need Tor to access it. It just looks like a normal website at a first glance. (Although somewhat ironic)
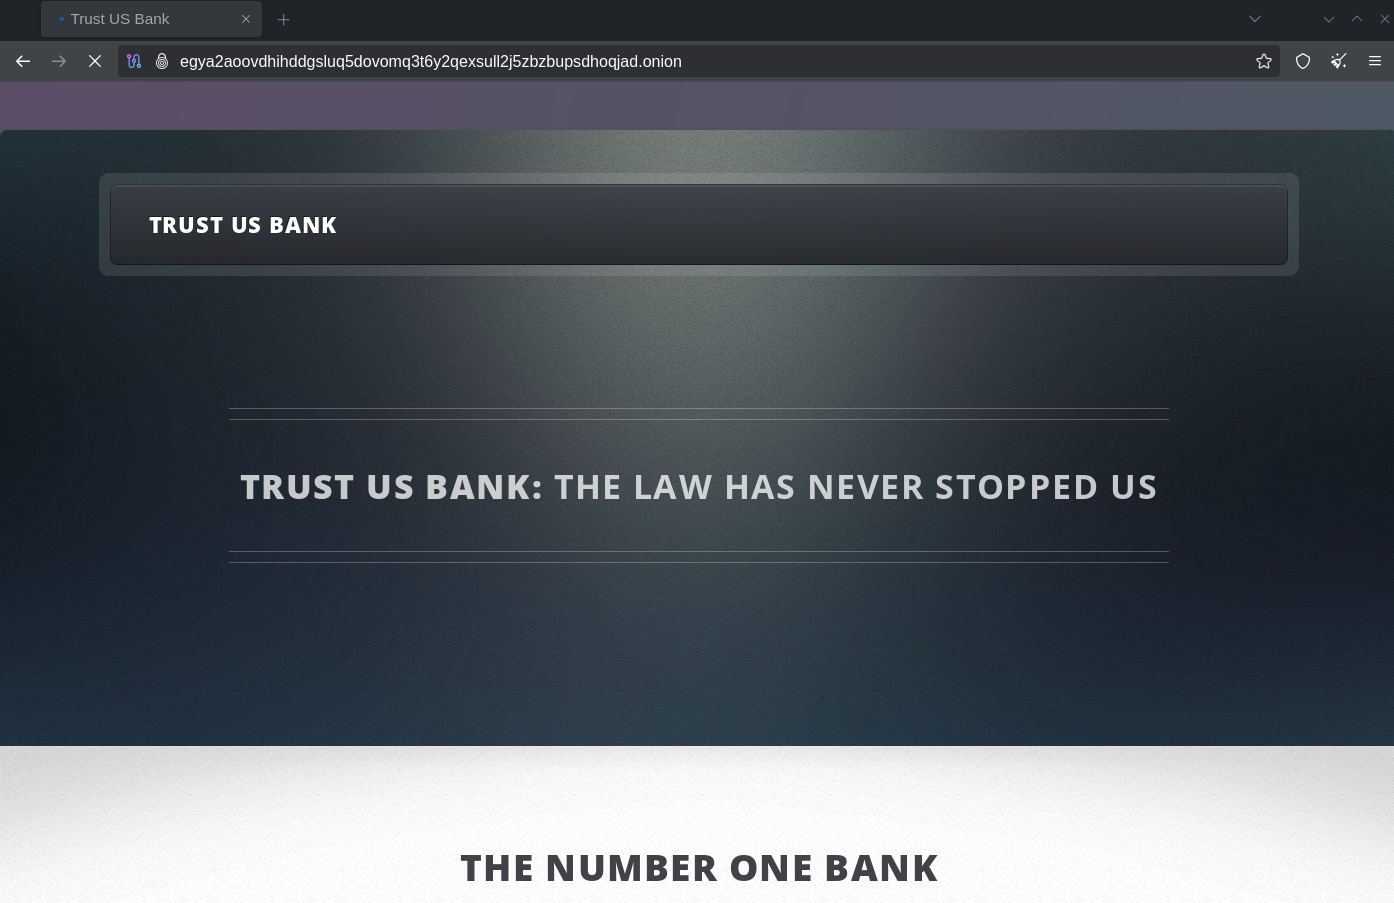
However, if we look for the sitemap (or robots.txt), we can find a mention for another page: /backdoor.html.
It is quite common to find assets here, as it instructs scrappers not to visit (or index) those pages.
Unfortunately, only few scrappers respect this directive nowadays.
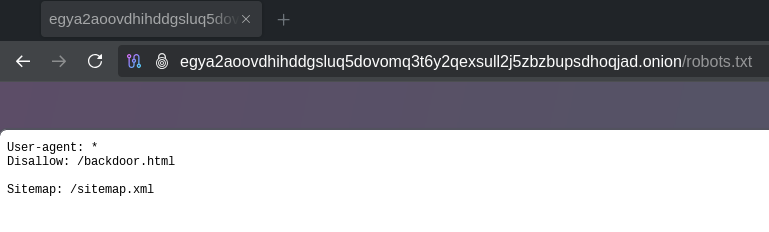
Indeed, if we visit it, we find a secret page !
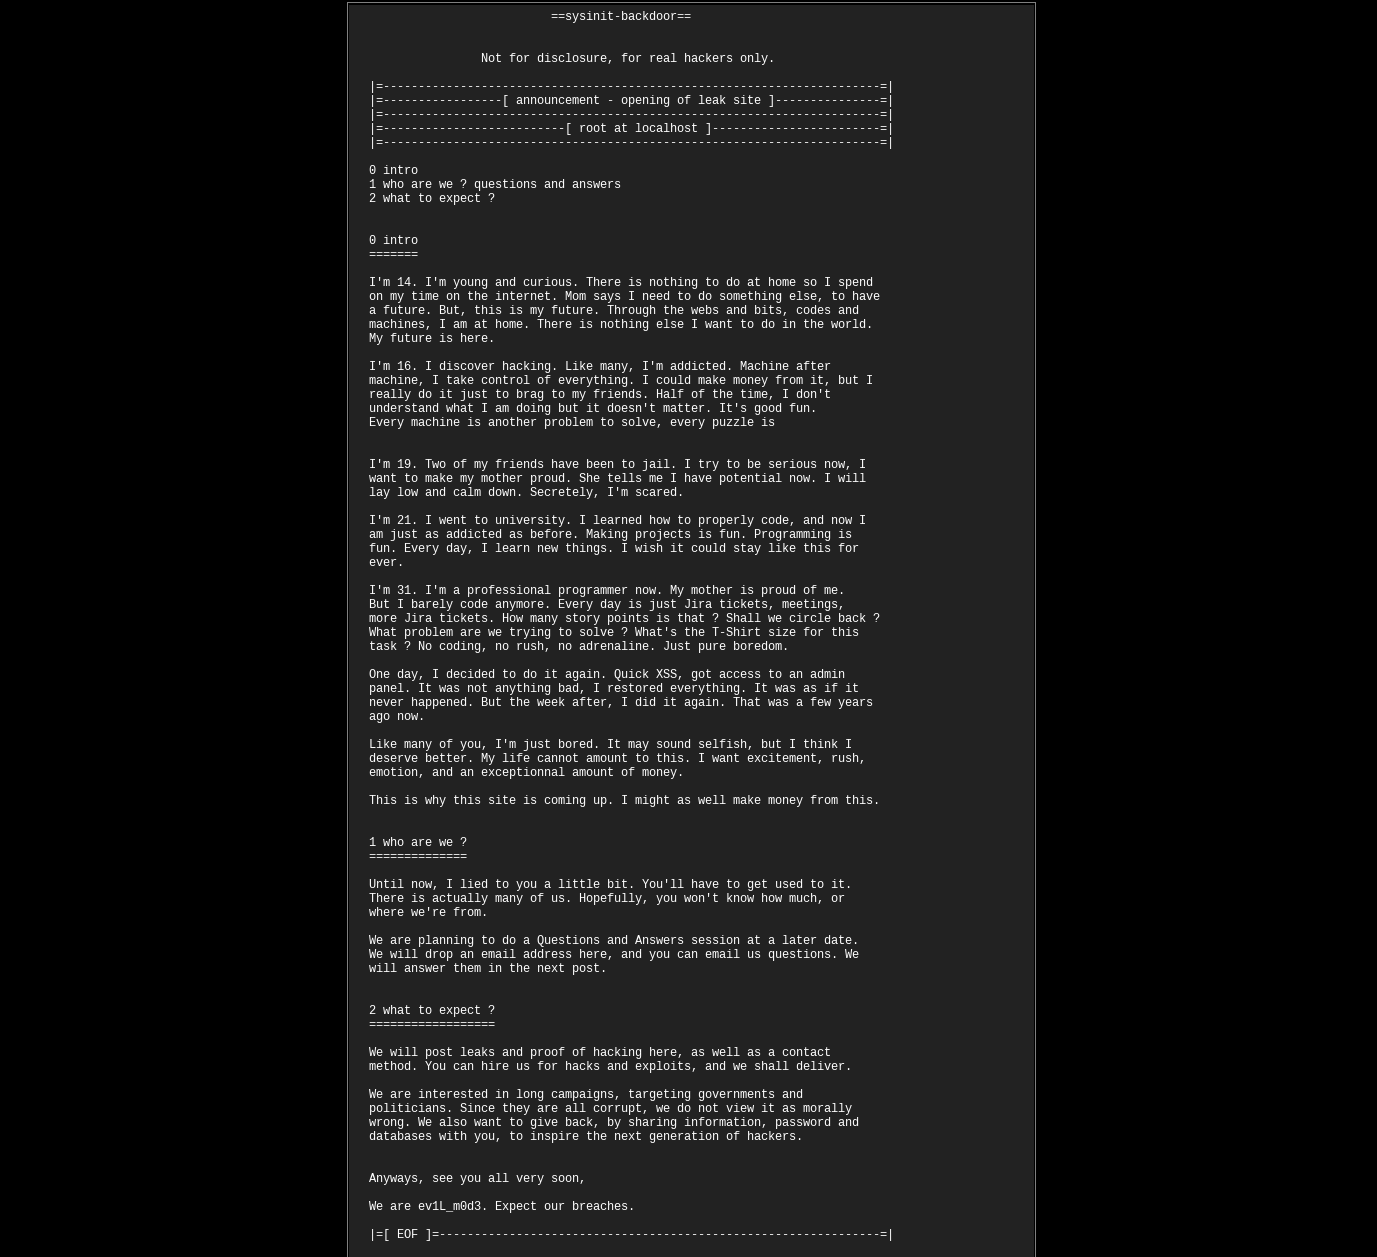
All the way at the bottom of the text, the name of the hacking group is given.
This is our fourth flag: tenguctf{ev1l_M0d3}
5. GEOINT
We have enough evidence to proceed with an arrest. It’s time to locate WINDSOR. Based on his accounts, identify where he could be right now.
As the name suggests, we’re doing some Geolocalisation here.
We need to find our target’s approximate location. Going back to his initial nickname, we find an associated soundcloud account, with an interesting picture as the banner:
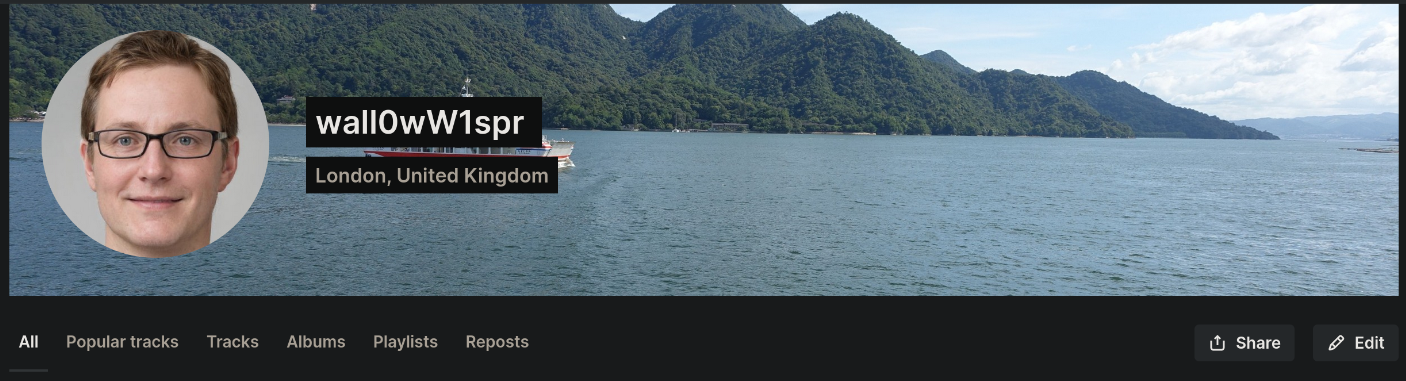
However, we cannot simply right-click to recover the banner.
You will need to Open “Inspect element”, reload the page, and grab the request that downloads the image. Here is it, for your convenience:
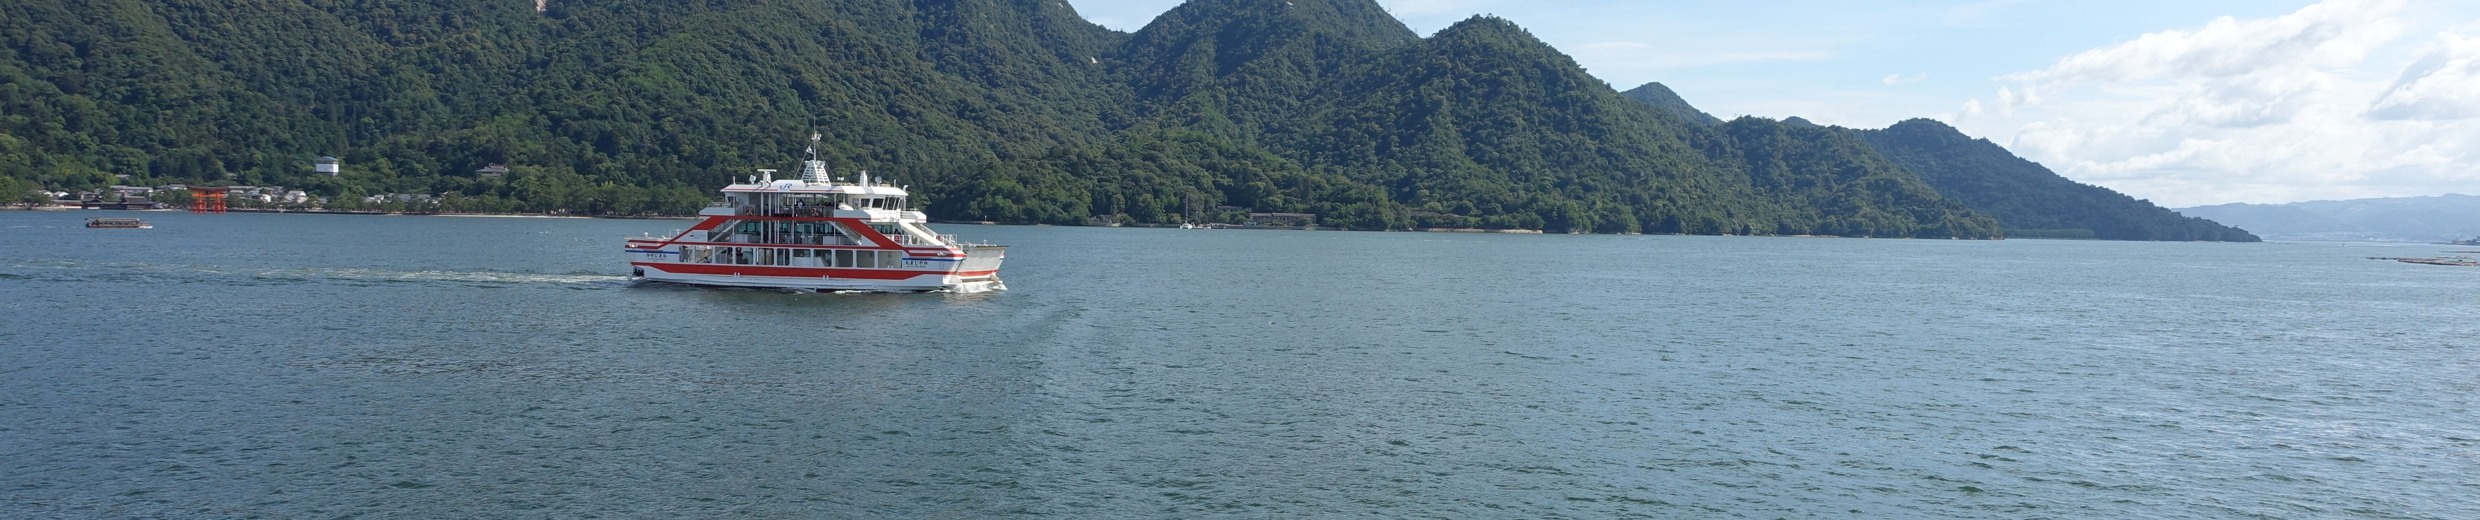
Zooming a lot, to the left, we see the famous Red Torii gates that are often found in Japan. However, we can see those are in the water, which is not typical. There is also a JR ferry. An LLM chatgot like Gemini or ChatGPT, will advise you that this is likely Miyajima, near Hiroshima, in Japan.
This is our fifth flag: tenguctf{Miyajima}
6. Just like on Netflix…
We are going to prepare a Social Engineering campaign using another of our agents, AGENT AERO.
To better approach WINDSOR, we need to find more intelligence about him. Since he’s a chess fan, find what is his favorite opening with white ?
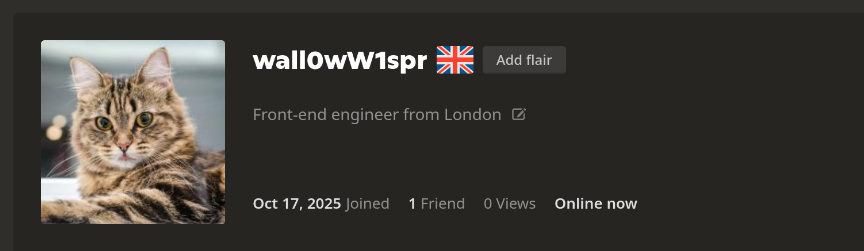
We can use on of those OSINT services to get our target’s chess.com account. Or, we can simply look for the username on Chess.com
We can confirm they’re owned by the same person because it shares the same profile image as the Gitlab account.
Looking at the history of games, we can find that pretty much all games played with white start with the move d2-d4. This is called the Queen’s Game, or the Queen’s Gambit.
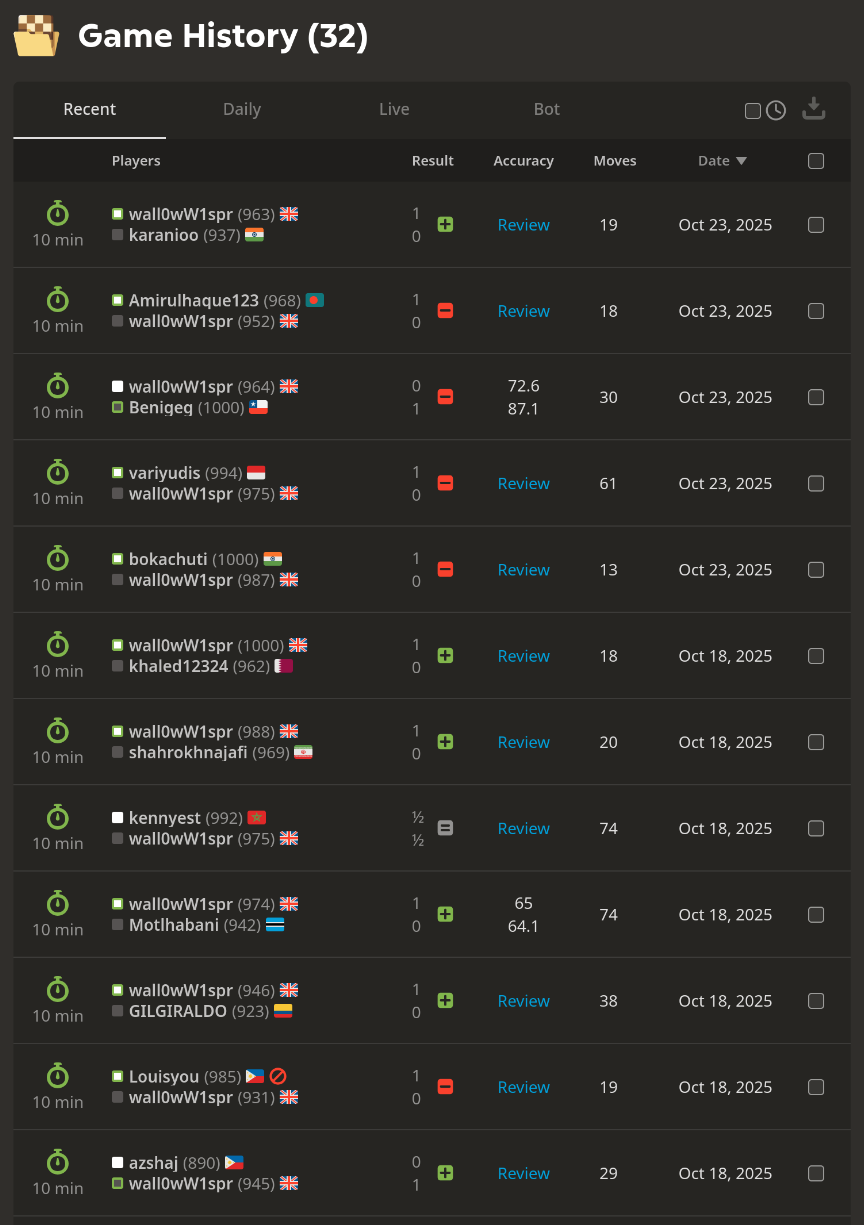
i know, i suck at chess.
Multiple flags are accepted here:
tenguctf{QueensGambit}tenguctf{QueensGame}tenguctf{QueensPawn}tenguctf{d2d4}
7. Preparing the arrest
AGENT AERO managed to make contact with WINDSOR. Our target is currently on vacation, but we will back soon. We need to arrest him at the airport, before he vanishes. Find which flight is WINDSOR going to take from the conversation:
AERO: Thanks for the games.

WINDSOR: You bet. Lichess is kinda nice. Had no idea you didn't need an account to play.

WINDSOR: Better for OPSEC.

AERO: Yeah.

WINDSOR: Alright. Thanks, man. I'll talk to you when I'm back in Europe.

AERO: When will that be ? I need to work soon, I need the money.

WINDSOR: Ahhh I understand. Don't worry, I have a couple of targets lined up. :)

AERO: When will we start man ?

WINDSOR: I'm back in Europe next week-end.

AERO: Are you flying from where you are ? I didn't know there was an international airport there)

WINDSOR: Haha, no. I'll take the ferry.

WINDSOR: Going to another country for two days. Then I'll fuck off from there on Friday.

AERO: That's cool. Are you taking a private jet, mr businessman ?))

WINDSOR: Lol, I wish. No. I have 38 hours of flight and a layover in Taiwan.

WINDSOR: Fucking kill me.

WINDSOR: At least I land in Heathrow, which is reasonnable.

AERO: wow

WINDSOR: Yeah. Overnight layover in Taiwan though. Not too bad, maybe I'll go out.

WINDSOR: Alright man, I'll talk to you later

AERO: Alright, see you)
We need to both flights WINDSOR will take to reach London. Please respond with the following format:
FL123-FL123. Then, we can proceed with the arrest.
Reading the conversation, we can find the following information:
- WINDSOR is flying on a friday, from a country adjacent to Japan,
- To get there, he is taking the ferry from Japan,
- The flight makes him land at Heathrow, with an overnight layover in Taiwan,
- The flight takes 38 hours in total (layover included)
The most common country to reach by ferry from Japan is South Korea. You can get the ferry from Fukuoka to Busan. Proceeding by elimination, we should be able to determine that the flight is the following:
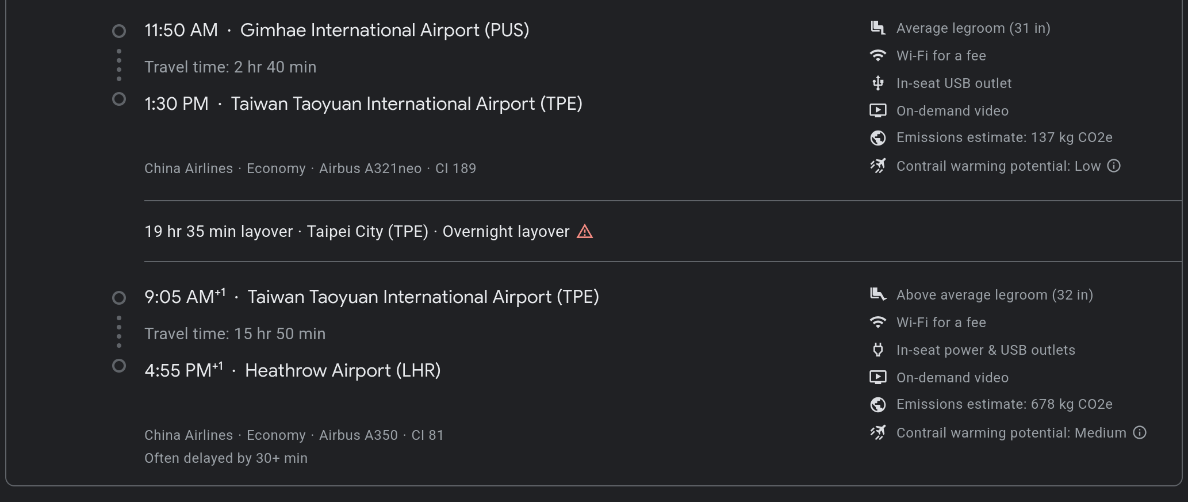
This is our final flag:
tenguctf{CI189-CI81}
Bonus challenge
Since I had a bit of time, I also contributed a reverse-engineering challenge. It is based on a rootkit I wrote (which I should probably finish one day…).
It is quite simple, it hooks kill, and if you pass it a succession of 19 kill calls with SIGUSR1, it will reveal a cool ASCII art !
Here is the solver:
#!/usr/bin/env bash


echo "[+] sending sequence"

# WhatIsYourPizzaStory -- if you don't know what the flag means, ask kamel;D
ASCII_CODES=(87 104 97 116 73 115 89 111 117 114 80 105 122 122 97 83 116 111 114 121)

for new_code in "${ASCII_CODES[@]}"; do
    echo "[+] killing [$new_pid]."
    kill -10 $new_pid
    sleep .2
done
I also made a little demo, that is available on Youtube.
Final words
And that concludes the series of challenges ! I hope the difficulty was linear, with easy challenges at the beginning, and it would gradually be harder. Feel free to reach out to give me your impressions if you attended, I am genuinely curious of whether it was too guessy or not.
But I will say that in general, making CTF challenges was really fun, and I hope I can keep doing that in the future.
See you next time :)~